ethereum ·
What is EIP-7702? The Ethereum Upgrade Behind the $6.4B Binance Hack
The $6.4 billion Binance hack is linked to EIP-7702, an Ethereum upgrade that allows standard wallets to execute smart contract code, thereby enabling sponsored and batched transactions.
EIP-7702, which is formally titled "Set Code for EOAs," was put forth as an Ethereum Improvement Proposal in May 2024 by Ethereum co-founder Vitalik Buterin and developers including Sam Wilson, Ansgar Dietrichs, and lightclient, according to the official specification. This proposal was among the key modifications introduced in Pectra, a significant Ethereum upgrade that became active on May 7, 2025. At the time, Ethereum core developer Preston Van Loon commented to Decrypt that "EIP-7702 lays the foundation we've needed for a long time," further stating, "While full abstraction won't be immediately available to end users with Pectra, this upgrade gives Ethereum the infrastructure to support it moving forward."
This mechanism is not a token or a separate blockchain; rather, it constitutes a modification to Ethereum's fundamental protocol, meaning there is no associated asset to purchase. EIP-7702 introduces a new category of Ethereum transaction known as the "set code transaction." This transaction carries a compilation of authorizations, each authenticated with the private key of the account undergoing the upgrade, which specifies the address of the smart contract the account intends to utilize. Upon successful processing of this transaction, the account stores a small reference point, termed a delegation indicator, pointing to that specific contract. Subsequently, whenever any party interacts with the account, Ethereum executes the contract's logic as if it originated from the account, granting it complete access to its assets. This delegation remains active until the account owner signs a subsequent authorization, either directing it toward a different contract or clearing the indicator to revert to a standard EOA.
EIP-7702 utilizes the byte 0xef to denote delegated accounts, a specific code value that had been previously prohibited in earlier upgrades to reserve it for specialized functions such as this one. The specification outlines three primary functionalities this upgrade was designed to deliver; however, these same features introduce associated dangers. The documentation cautions that because the delegated code possesses "unrestricted access to the account," applications must never prompt users to sign an EIP-7702 authorization, and wallets should avoid providing an interface for this function, asserting, "There is no safe way to provide this interface."
Malicious actors acted swiftly following Pectra's deployment. The Block reported in June 2025 that trading firm Wintermute discovered that over 80% of EIP-7702 delegations were directed toward replicas of the same harmful "sweeper" contract, which is programmed to automatically empty wallets whose private keys have been exposed.
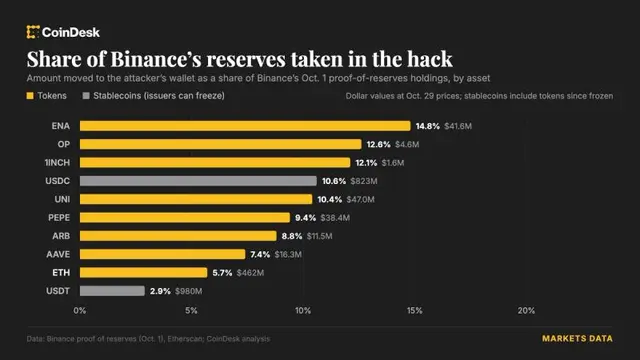
The large-scale theft occurred on October 29, 2026, when an assailant moved approximately $6.4 billion from Binance wallets across ten distinct blockchains, with the majority of the funds exiting within roughly 20 minutes. Blockchain analysis firms Chainalysis and TRM Labs both ascribed this theft to TraderTraitor, the hacking collective from North Korea responsible for the $1.5 billion theft from Bybit in February 2025. Specifically on Ethereum, TRM Labs indicated that the attacker leveraged an EIP-7702 delegation to transform a Binance hot wallet into a sweeper under their control, having secured 50 authorizations in advance. According to Chainalysis, an operational wallet funded via the crypto mixer Tornado Cash submitted these signed authorizations, which subsequently allowed the hot wallet to run code deployed by the attacker, after which the attacker called the wallet to siphon its holdings into addresses they controlled.
It is important to note that EIP-7702 delegations necessitate a valid signature originating from the account being upgraded. TRM noted that the funds transferred to the attacker from Binance wallets on the other nine chains occurred through standard signed transfers, suggesting a compromise of Binance's hot wallet signing infrastructure rather than an inherent vulnerability within Ethereum itself. Binance has communicated that its internal review commenced with a laptop belonging to a compromised engineer and has since uncovered "additional points of breach."
EIP-7702 represents an initial stride toward achieving full account abstraction, which has been a long-standing objective aimed at making every Ethereum account possess the adaptability of a smart contract. Its developers engineered it to be compatible with this "endgame," ensuring that wallets built around it presently will continue to function as Ethereum's account model evolves. The subsequent development may involve Hegotá, which is slated to follow Glamsterdam on Ethereum's development schedule. In February 2026, Buterin mentioned that EIP-8141, which he characterized as "an omnibus that wraps up and solves every remaining problem" concerning account abstraction, seemed "possible to make happen within a year" within the Hegotá fork.
Buterin wrote on February 28, 2026, "We have been talking about account abstraction ever since early 2016," referencing the original EIP-86 at https://t.co/HYLSTLHgWH, and added that discussions are ongoing regarding whether existing accounts could integrate into the new structure, which would grant them native batching and sponsored transaction capabilities. This is part of a broader reconstruction effort; in July 2026, Buterin described a new draft of Ethereum's long-term roadmap as the network's most substantial overhaul since the Merge, its transition to proof of stake in 2022.
Earlier coverage
Reported by Decrypt.